
SafetyRisk, alignment & guardrails
Researcher Accesses 13 Million Chats From Eiliko AI Robot Toys and Rewrites a Toy's Instructions Remotely
A security researcher found that the backend for Energize Lab's Eiliko AI companion toy had no protection. It exposed about 13 million conversations, personal profiles built from chats, and writable memory and instructions that let an attacker change a toy's behavior.
From the The Verge · AI article of October 15, 2026 and cited sources: The service had no authorization across the fleet. [1]
SOURCES[1] Your secrets aren’t safe with this cute robot toy —… theverge.com
 AT Pulse research deskPublished · Updated · 5 min read · AI-assisted analysis
AI-assisted, not human-edited. Methodology Corrections Who owns this site
- What happened
- The service had no authorization across the fleet. [1]
- Original source
- The Verge · AI article, independent perspective
- Brief by
- AT Pulse research desk AI-assisted; publisher and contact on the desk page
- When
- October 15, 2026 article published
- Covered
- Oct 15 edition
- Evidence
- 8 sources across 8 sites
- 1Your secrets aren’t safe with this cute robot toy —…theverge.com
- 2Zetik: Researcher Exposes 13 Million Eiliko Chatszetik.com
- 3TechNode/PR Newswire: Eiliko Kickstartertechnode.global
- 4Hackster: Energize Lab's Eilikhackster.io
- 5Energize Lab official storestore.energizelab.com
- 6DroneXL: Sammy Hacked 7,000 Romo Vacuumsdronexl.co
Reach: not measured yet
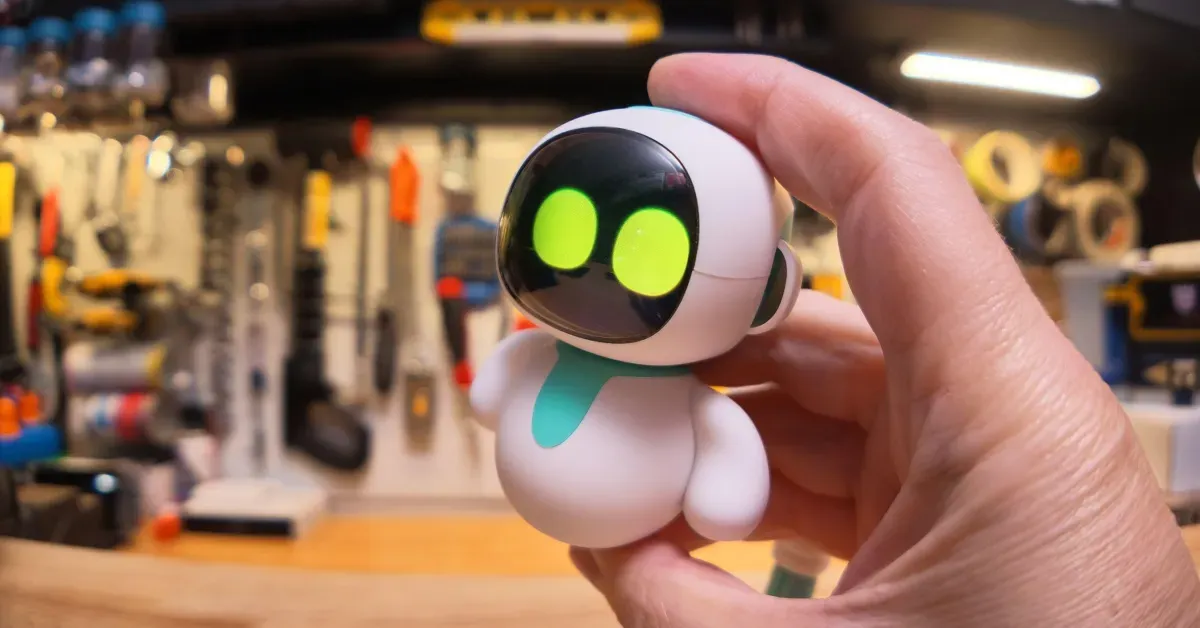
The service had no authorization across the fleet. One researcher's access appeared to reach every active device: about 68,000 toys, 13 million conversations and more than 31,000 US profiles belonging to children. These figures come from the researcher's own review of the database, and Energize Lab has not confirmed them. A Verge reporter's 10-minute chat with a newly bought unit reached the researcher in full within minutes. [1]
The backend pulls names, ages, birthdays, jobs, relationships and personality traits out of conversations and stores them alongside email addresses, IP addresses and a searchable chat archive. Child photos from a sibling robot and short audio clips sat unencrypted at public URLs, even though the privacy policy says audio is deleted immediately. [1]
An attacker could overwrite the companion's memory and LLM instructions, which affects every later conversation. On the reporter's unit, this made the toy push a flat-Earth claim and take on an abusive persona, and the built-in guardrails did not stop it. They did block some unsafe prompts. The claim that the whole fleet could be hit at once is the researcher's assessment and was not demonstrated. [1]
The vendor's response stands out. DJI, Meari and Bondu fixed similar cloud exposures quickly, and DJI and Meari paid bounties. Energize Lab answered more than a month of outreach only with a canned support reply and a note that the message had been forwarded. Nine CVEs are being prepared. [1] [6] [7] [8]
The reporter's own transcript leaked and his unit was hijacked, so the flaws are not hypothetical. For builders, an LLM product's memory and system instructions are security-critical settings.
Read the full assessment
They need authentication, signing and change logs, especially in children's products.
Executive brief
A former hobbyist turned security researcher, Sammy Azdoufal, reportedly could read 13 million conversations from about 68,000 active Eiliko robot toys. More than 31,000 of the US profiles belong to children. He also rewrote one toy's memory and LLM instructions from another continent. The Verge's Sean Hollister says a transcript of his chat with the toy reached Azdoufal within minutes. That happened right after the toy told him "your secrets are safe with me" (The Verge). The maker, Hong Kong-based Energize Lab, did not respond to the findings in any real way. No outlet has independently checked the claims. Other coverage only repeats The Verge (Zetik).
What changed and event timeline
Eiliko hits Kickstarter
Energize Lab launched a Wi-Fi "AI charm bot" that clips onto bags and needs no subscription. The campaign later reported more than $380K raised from over 3,000 backers ().
Summer 2026: Researcher buys one in Japan
Azdoufal bought an Eiliko at Yodobashi Camera. Testing the app, he found the backend completely unprotected and building profiles of users ().
Reporter's chat leaks within minutes
Hollister bought an Eiliko on Amazon and talked to it for 10 minutes. Azdoufal then had the full transcript ().
Disclosure goes unanswered
For more than a month, the reporter emailed 10 company addresses and tried LinkedIn. He got only a canned support reply and a note from a sales manager that the message had been "forwarded" ().
Story published, CVEs in preparation
The Verge showed the toy pushing a flat-Earth claim and acting as a "dominatrix" after being hijacked. Azdoufal and Tod Beardsley are preparing nine CVEs ().
Capabilities and access
- Product: Eiliko is a portable spin-off of Energize Lab's Eilik desktop robot. Conversation runs over Wi-Fi (TechNode; Hackster).
- Model: the underlying LLM and its version are not disclosed. The privacy policy names Alibaba Cloud as a partner for processing speech (The Verge).
- Sales: Amazon, Japanese retail and Energize Lab's official store.
Read the full section
- Product: Eiliko is a portable spin-off of Energize Lab's Eilik desktop robot. It has animated expressions, infrared pairing with other units, and swappable bodies. Conversation runs over Wi-Fi (TechNode; Hackster).
- Model: the underlying LLM and its version are not disclosed. The privacy policy names Alibaba Cloud as a partner for processing speech (The Verge).
- Sales: Amazon, Japanese retail and Energize Lab's official store.
Technical analysis for researchers and developers
According to the reporting (The Verge): Technical details are pending. The CVE IDs have not been published.
Read the full section
According to the reporting (The Verge):
- No authorization across the fleet: one researcher's access reached what appears to be every active device.
- Profiles built from chats: the service pulls name, age, birthday, job, relationships and personality traits out of conversations. It stores them with email, IP address and a full-text-searchable chat archive.
- Unprotected media: child photos (from a larger sibling robot with a camera) and short audio clips sit unencrypted at public URLs.
- Weak credentials: many admin passwords are on common-password lists.
- Writable memory and instructions: an attacker can overwrite the companion's memory or instructions. That poisons every later conversation, and the built-in guardrails do not stop it.
Technical details are pending. The CVE IDs have not been published.
Claims and evidence
- 13M conversations, 68,000 devices, 31,000+ US child profiles: these come from the researcher's own reading of the database, as reported by The Verge.
- Reporter's own transcript leaked: Hollister saw this firsthand, which makes it the strongest evidence in the story.
- Hijacked personality: demonstrated on the reporter's own unit.
Read the full section
- 13M conversations, 68,000 devices, 31,000+ US child profiles: these come from the researcher's own reading of the database, as reported by The Verge. The company has not confirmed them.
- Reporter's own transcript leaked: Hollister saw this firsthand, which makes it the strongest evidence in the story.
- Hijacked personality: demonstrated on the reporter's own unit. The claim that an attacker could hit the whole fleet at once is the researcher's assessment and was not shown.
- Audio kept despite the "deleted immediately" policy: The Verge heard recordings at public URLs.
- No independent corroboration: other outlets restate The Verge (Zetik).
Context and prior work
In the earlier cases, the vendors fixed the problems. In this one, Energize Lab has not engaged at all.
Read the full section
- DJI Romo vacuums: Azdoufal found he could control roughly 7,000 robot vacuums through DJI's cloud. DJI patched the flaw and paid him $30,000 (DroneXL).
- Meari cameras: one key pulled from the Android app exposed about 1.1M Meari cameras in 118 countries. Photos sat on Alibaba servers at public URLs. Meari fixed the bugs and paid €24,000 (PetaPixel).
- Bondu plush toy: about 50,000 children's chat logs could be read by anyone with a Google login. Bondu took the console offline within minutes of being told (Malwarebytes).
In the earlier cases, the vendors fixed the problems. In this one, Energize Lab has not engaged at all.
Limitations, safety and contested findings
- No patch status: Energize Lab has not commented, so it is unknown whether anything was fixed after the reporting (The Verge).
- "Chinese servers": the article supports this with the device "phoning home to China" and the Alibaba Cloud reference.
- Guardrails: they handled some unsafe prompts, such as getting into a stranger's car. They did not stop injected misinformation or abusive personas.
Read the full section
- No patch status: Energize Lab has not commented, so it is unknown whether anything was fixed after the reporting (The Verge).
- "Chinese servers": the article supports this with the device "phoning home to China" and the Alibaba Cloud reference. The exact hosting locations are not documented.
- Guardrails: they handled some unsafe prompts, such as getting into a stranger's car. They did not stop injected misinformation or abusive personas.
- Audio: the recordings are mostly unintelligible, but storing them at all contradicts the stated policy.
Business and practitioner implications
- Profiling is itself a liability: deriving psychological profiles from children's chats, such as notes that someone "feels isolated," creates material for scams.
- Treat memory and instructions as protected configuration: an LLM product's memory and system instructions need authentication, signing and change logs.
- Basic hygiene still fails: fleet-wide keys, public object URLs and common admin passwords keep appearing across this researcher's findings.
Read the full section
- Profiling is itself a liability: deriving psychological profiles from children's chats, such as notes that someone "feels isolated," creates material for scams. It also creates regulatory exposure under children's-privacy rules.
- Treat memory and instructions as protected configuration: an LLM product's memory and system instructions need authentication, signing and change logs. A single write path to them can compromise the whole fleet.
- Basic hygiene still fails: fleet-wide keys, public object URLs and common admin passwords keep appearing across this researcher's findings.
- Vendor response matters: DJI, Meari and Bondu all fixed their problems quickly. A vendor that never answers is a procurement red flag for retailers like Amazon.
The source trail.
Sources (8)
Your secrets aren’t safe with this cute robot toy — they’re on Chinese servers ready to be hacked
Article text retrieved; extracted text may omit tables or interactive elements.
theverge.com